What Is Hack for Humanity, and How Do Social Good Hackathons Work?
Hack for Humanity is a name several organizations use for hackathons that point software at a social …
Read More
Six practical tips for cybersecurity hackathons: CTF practice, ethical scope rules, team roles, defensive projects, and how sponsors can fund safe security events.
A cybersecurity hackathon is a time-boxed event where teams build security tools, attack and defend practice systems, or solve security puzzles under a deadline. Some run as capture the flag (CTF) competitions, where players find hidden strings called flags inside deliberately vulnerable challenges. Others work like product hackathons: teams build a defensive tool, a detection rule set or a privacy feature, then demo it to judges.
This round-up is for people who already know what a hackathon is and want to do well at the security-flavored kind. That includes Philadelphia developers looking for cybersecurity hackathons near them, bootcamp graduates who want security work in a portfolio, and the sponsors and donors who make these events safe and free to attend. We run weekly coding sessions and quarterly hackathons at C.O.D.E Philadelphia, and these tips come from what we see builders and backers get right.
Security events differ from other hackathons in one important way: the skills you practice can cause real harm if pointed at the wrong target. That changes how you prepare, how you scope a project and how organizers write the rules. The six tips below follow that thread.
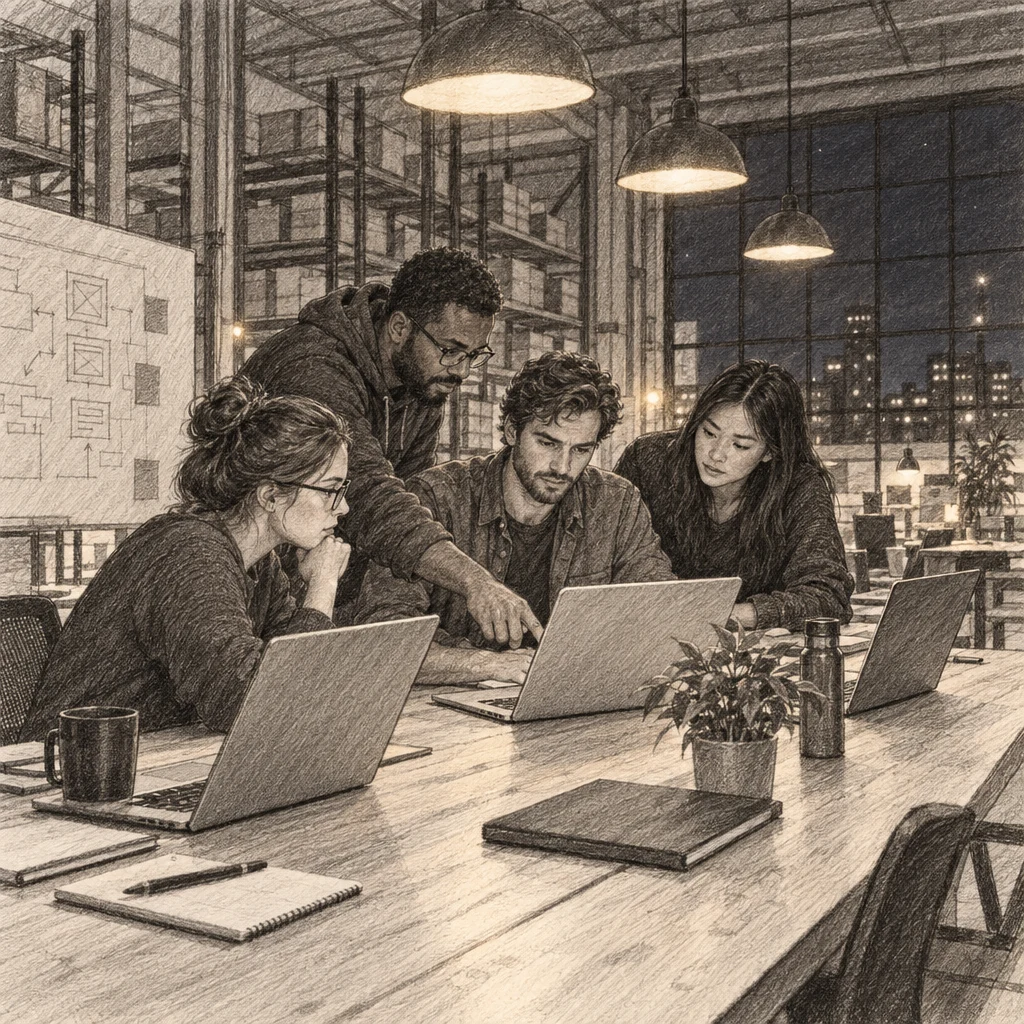 Security challenges go faster when teammates can talk through an exploit or a fix side by side.
Act on this first: read the event’s scope and rules of engagement before you plan anything. In a cybersecurity hackathon, testing a system you were not given permission to test can break the law and get you removed, even if your intent was good.
Only touch what the organizers hand you. Every well-run security event lists which systems, IP ranges and challenge servers are in scope. Anything outside that list is off limits, including the venue Wi-Fi, other teams’ machines and the scoring server itself unless the rules invite it.
Accessing a computer system without authorization can violate the Computer Fraud and Abuse Act or other laws, and a hackathon badge does not change that. Clear scope is what separates practice from intrusion. It also protects organizers, who carry the liability when an attendee goes off the map.
CTF practice is the fastest warm-up for security hackathons. Most security challenges fall into familiar categories: web exploitation, cryptography, reverse engineering, binary exploitation, forensics and miscellaneous puzzles. Solving a few of each before the weekend means you recognize the pattern instead of learning it under a clock.
The capture the flag format has two main styles. Jeopardy-style CTFs give a board of challenges worth different points. Attack-defense CTFs give each team a service to protect while attacking the others’ copies. Knowing which style an event uses tells you whether to prepare for puzzles or for patching under pressure.
Free, legal practice targets exist for exactly this purpose. Deliberately vulnerable apps such as OWASP Juice Shop run on your own laptop, so nothing you break belongs to anyone else. Many universities and security clubs also publish past CTF challenges with write-ups.
Build something that protects, then show it working on your own test setup. Not every cybersecurity hackathon is a CTF. Build-style events reward tools: a phishing link checker, a secrets scanner for code repositories, a log anomaly detector or a password policy auditor. Judges can see these work in a live demo without anyone attacking a real system.
Defensive projects also travel better into a job search. An employer can read your repository and run your tool. A short attack demo against a sandbox you built yourself is fine, as long as you can show the target is yours. The same thinking applies to AI security: at our AI Agent Hackathon, a team testing prompt injection against its own agent is doing legitimate security work.
Here is a small example of a demo-ready tool: a few lines of Python that flag likely AWS access keys in a file. A team could grow this into a pre-commit hook in one weekend.
import re, sys
pattern = re.compile(r"AKIA[0-9A-Z]{16}")
for n, line in enumerate(open(sys.argv[1]), 1):
    if pattern.search(line):
        print(f"Possible key on line {n}")
The first line loads the regular expression and system modules. The second defines the pattern AWS uses for access key IDs. The loop reads the file named on the command line, and the last line prints the line number of any match. Swap in more patterns and you have a scanner to demo.
Assign people to challenge categories, not just front end and back end. In a CTF, a team that splits the board by category covers more ground than a team that swarms one problem. In a build event, someone should own the threat model while others write code.
Early-career developers often undersell themselves here. A web developer already understands cookies, sessions and HTTP headers, which is most of web exploitation. A data person reads logs well, which is most of forensics. Mixed teams are an advantage.
Matching a builder’s background to a security role
| Background | Strong fit | First thing to practice |
|---|---|---|
| Web developer | Web exploitation | Injection and broken access control |
| Systems or C programmer | Binary exploitation, reversing | Reading disassembly |
| Data or analytics | Forensics, log analysis | Packet captures and log parsing |
| Math or CS theory | Cryptography | Classical ciphers and weak keys |
| Designer or PM | Threat modeling, demo story | Writing a clear attack narrative |
The best way to hear about a cybersecurity hackathon in 2026 is to be in the room where builders talk. Security events are often announced inside communities before they hit public listings: university clubs, local security meetups and developer groups. Showing up weekly puts you on those lists.
Interest in these events is real when someone organizes them well. For the Hadatha Cybersecurity Industry Hackathon in Oman, 165 individuals applied to register and 50 ideas were submitted in a ten-day registration window in 2024. That event pointed participants at industry problems, which is a useful model for city-level events in 2026.
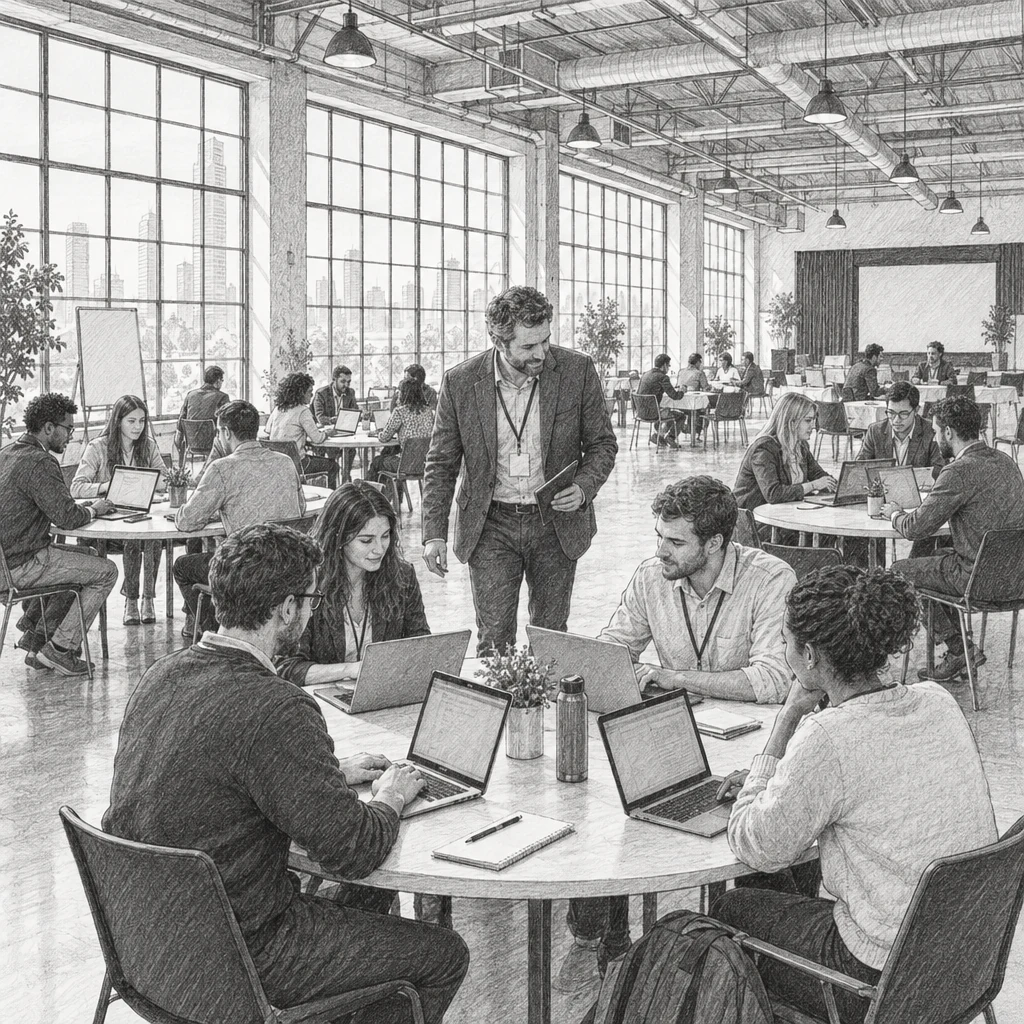 In-person hackathons give security newcomers mentors they can ask in real time.
Your money makes security learning safe and free. A cybersecurity hackathon needs isolated infrastructure: cloud sandboxes, challenge servers and network setups that keep practice traffic away from real systems. It also needs experienced mentors who can answer scope questions on the spot. Both cost money that ticket-free community events cannot cover alone.
For CSR program managers, this is a clear outcome to fund. Philadelphia builders, including bootcamp graduates without a security employer behind them, get hands-on practice that usually sits behind paid training. Sponsors can also contribute challenge ideas drawn from their own (sanitized) security problems, which gives teams realistic work and gives your security team a view of local talent.
Want more Philadelphia builders practicing security the right way? Join C.O.D.E Philadelphia at a weekly coding session or our next quarterly hackathon, volunteer as a mentor, or sponsor a sandbox so the next team learns to defend real systems without ever touching one.
Powered by gofylo.io